Cribl SIEM Alternative: Cribl Detect or the SIEM you already have - Realm Security blog

Cribl SIEM Alternative: Cribl Detect or the SIEM You Already Have?

Read More
Splunk SIEM Pricing Explained - how to cut your Splunk costs, from Realm Security

Splunk SIEM Pricing Explained (+ How to Cut Costs)

Read More
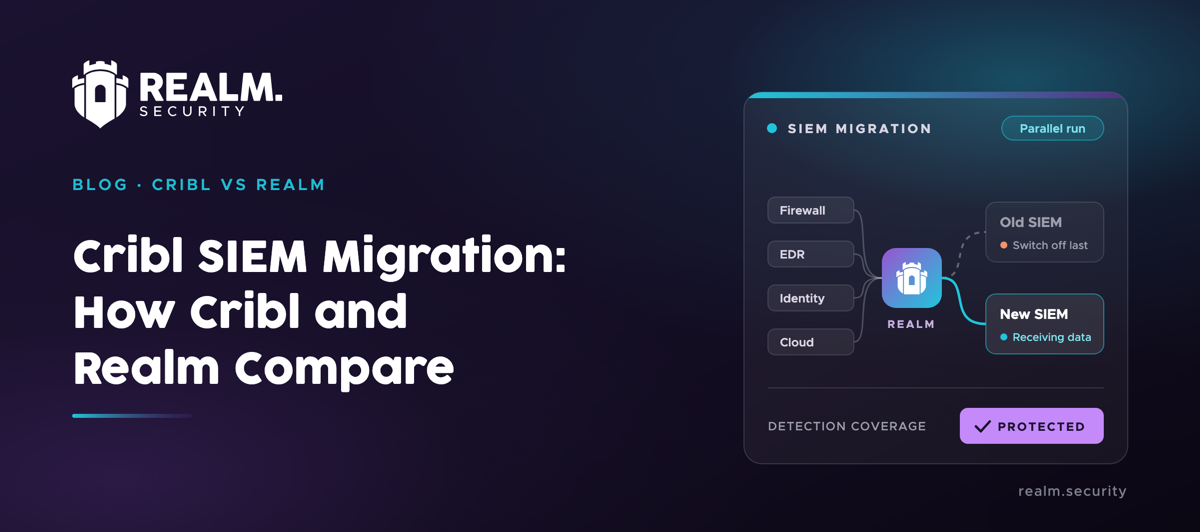
Cribl SIEM migration - how Cribl and Realm compare, with Realm routing security sources to an old and a new SIEM while detection coverage stays protected

Cribl SIEM Migration: How Cribl and Realm Compare

Read More
Realm Security and Scanner logos side by side on a dark background

Realm Security + Scanner: The Data Layer for an AI-Led SOC

Read More
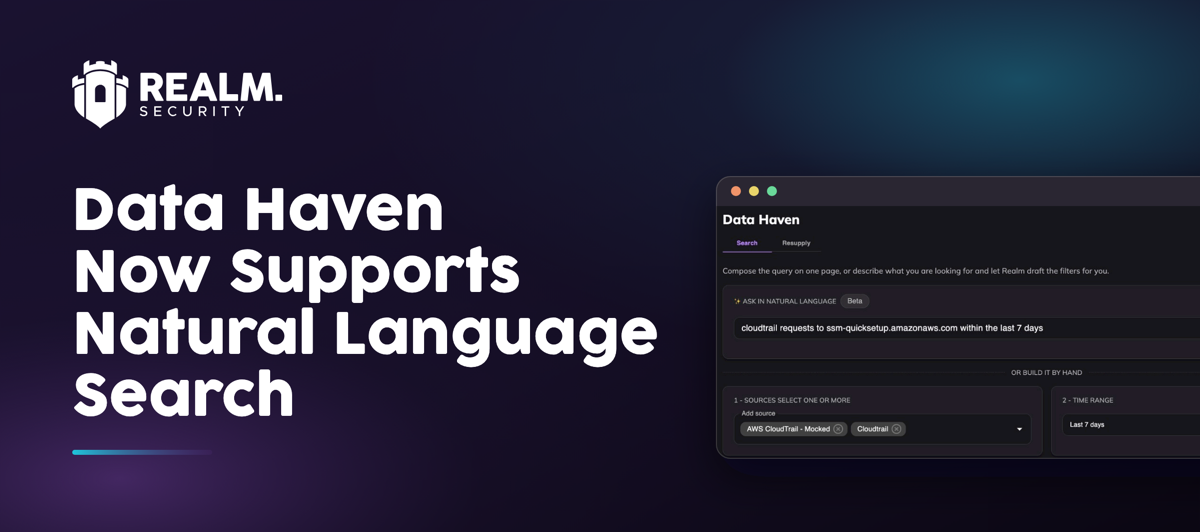
Data Haven Now Supports Natural Language Search - the Data Haven Search page in Realm with a plain-language request for CloudTrail events

Data Haven Now Supports Natural Language Search

Read More
Migrating From Splunk to Microsoft Sentinel? 5 Questions to Ask Before You Move - Realm routes firewall, EDR, identity and cloud data to Splunk and Microsoft Sentinel in parallel

Migrating From Splunk to Microsoft Sentinel? 5 Questions to Ask Before You Move

Read More
Microsoft Sentinel Migration: 6 Questions to Ask Before Your Move - Realm routes firewall, EDR, identity and cloud data to the current SIEM and Microsoft Sentinel in parallel

Microsoft Sentinel Migration: 6 Questions to Ask Before Your Move

Read More
How to Switch SIEMs Without Compromising Detection Coverage - Realm routes firewall, EDR, identity and cloud data to the current and the new SIEM in parallel so detection coverage can be matched before cutover

SIEM Migration Guide: How to Switch SIEMs Without Compromising Detection Coverage

Read More
Cyber Roundtable - Greg Crowley - Runtime Executive

Governance Theater: Greg Crowley on Governing AI

Read More
SIEM log management with a security data pipeline — normalize, filter, protect, and route logs before the SIEM with Realm.Security

SIEM Log Management With a Security Data Pipeline

Read More